From authorization
to return.
A short path for the user, with every state that matters recorded by the system.
Authorize
An administrator grants a person, or a whole authorization group, the right to open specific slots.
Verify
The user authenticates at the cabinet terminal by face, palm, fingerprint, card or PIN.
Take
Only the authorized slot unlocks. The cabinet records that the key left the hook.
Use
The key is used for the approved vehicle, room or piece of equipment.
Return
The key goes back on a hook and the cabinet closes the transaction automatically.
Designed around what actually goes wrong.
Most of the day is uneventful. The value is in what the system does on the days it is not: a key that never comes back, a door left hanging open, a cabinet that drops off the network.
A key out past its allowed time raises an alert that stays open until somebody resolves it.
The cabinet reports a slot door left open past the firmware threshold.
A cabinet that stops reporting shows up on the duty console, not in a log nobody reads.
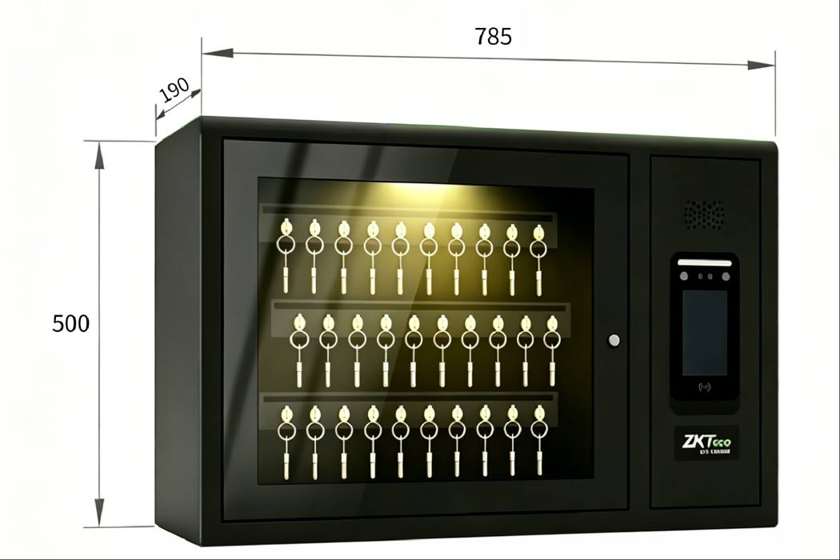
Nothing extra for the person at the cabinet.
Walk up, authenticate, take the key. No app to open, no sheet to sign, no supervisor to find. Everything the system needs, it captures by itself.
Authorized users keep opening their slots. Records sync once the cabinet is back online.
Role changes and departures withdraw slot access without anyone visiting the cabinet.
Change the slot count on the cabinet and the software reconciles it, without re-registering the device.